From cyber strategy
to real impact.
Johan Rambi advises boards and senior executives of critical infrastructure. He turns IT and OT cyber risk into clear decisions, and helps your organisation carry them out.
Cyber risk is now a board matter.
NIS2 makes directors personally accountable for cyber risk management, yet what reaches the boardroom is often technical, long and hard to act on. I translate risk into choices a board can make: what is at stake, what it costs, and what needs to happen first.
Clarity
A risk picture the board recognises and can steer on.
Governance
Clear ownership, from the boardroom to the plant floor.
Resilience
Security that holds up across people, process and technology.
Six ways I work with leadership teams.
Most assignments combine several of these. Select one to see what it involves.
Board advisory
An independent sparring partner for boards, supervisory boards and executives. Cyber risk explained in business terms, and a strategy the organisation can carry.
IT/OT experience in practice
- FrieslandCampinaDairy production
Supports the CastleGuard programme to set up an Enterprise Cyber Defence Center for office IT and production OT systems, and to build an integrated IT/OT security monitoring platform. Also supports the CISO office with cyber risk management, cyber insurance and other (interim) activities.
- KenterEnergy infrastructure
Supported Kenter as security architect during the carve-out, separating its systems from Alliander and onboarding an MSSP for the SOC services. As interim CISO for KenterGroendus, built a CISO office and set up an integrated IT/OT security roadmap.
- LianderElectricity and gas grid
Privacy & Security Officer at one of the largest Dutch grid operators, where grid operations, metering and customer data meet.
- Offshore windRemote-controlled assets
Bringing offshore asset owners and grid operators together to share security knowledge and information in the trusted community environment of the European Energy-ISAC.
- Eastern EuropePower grids
Working with grid operators in the Black Sea region to set up a Black Sea Energy ISAC, where they share security knowledge and information in a trusted community environment. Also advised on smart meter and smart grid cyber security systems.
Four steps from strategy to impact.
Advice only counts when it changes what an organisation does. Every assignment moves through the same four steps, and I stay involved until the change holds.
Assess
Where do you stand? Maturity, risks and obligations in one picture.
Prioritise
What matters most? A roadmap the board approves and can steer on.
Build
Policies, controls, monitoring and the people to run them.
Embed
Governance, reporting and exercises that keep resilience going.
One sector, one shared defence.
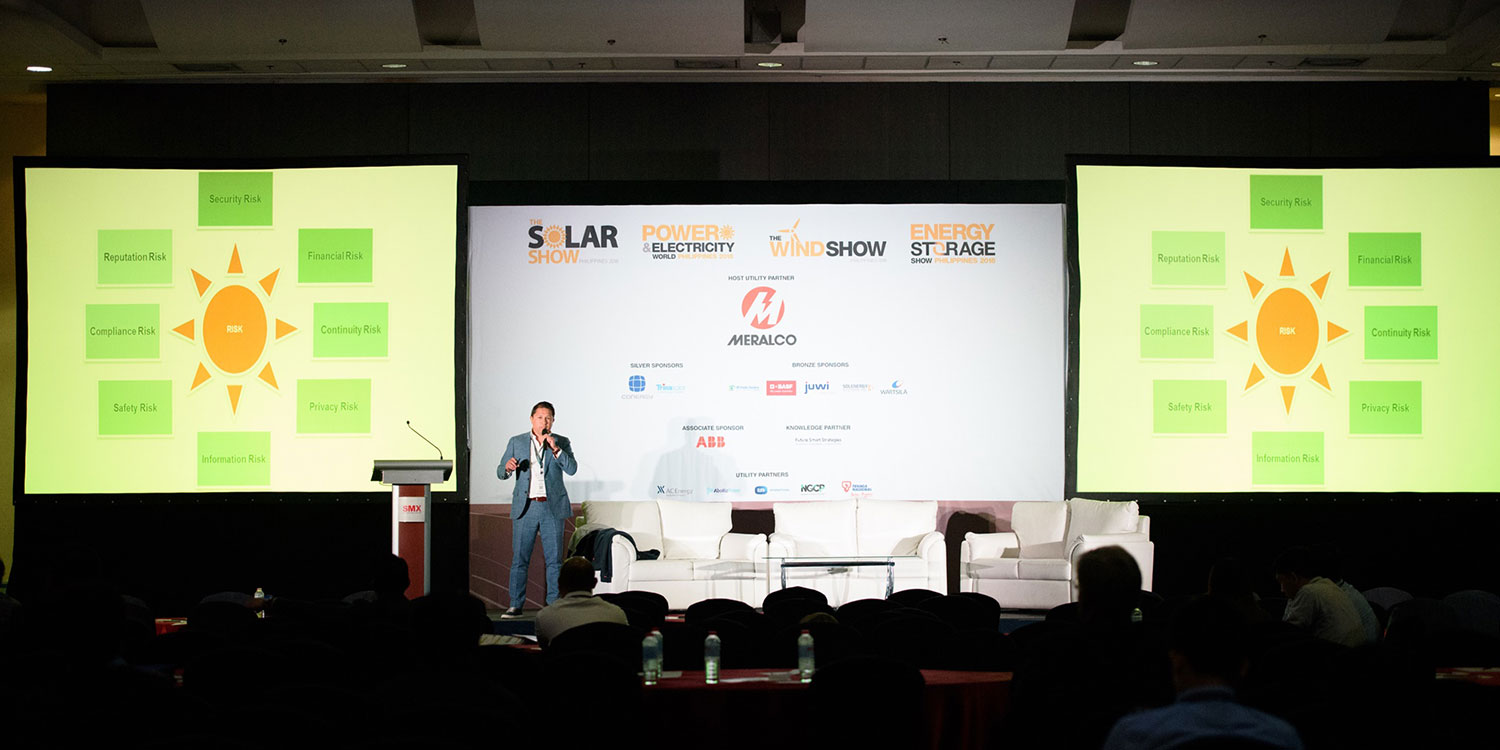
Attackers reuse their methods across a sector. Defenders who share information spot them sooner. Since 2013 I have built communities where organisations, often competitors, exchange what they see: incidents, attack patterns, weak spots in shared suppliers. In Europe, with partners in the US and Japan, and in new Dutch sectors such as offshore wind.
Europe
Co-founder of the European Energy-ISAC, the information-sharing community for Europe's energy sector.
US and Japan
Collaboration agreements between leading sector ISACs, recognised at the G7 Cyber Security Summit.
Netherlands
Founder of the Agrifood-ISAC and the EVC-ISAC for EV charging. Initiated communities for Solar & Storage and Offshore wind.
Senior, independent, in the field.
Johan Rambi founded RambiCo in 2018 to work directly with the people who decide: boards and senior executives who want cyber risk explained plainly and acted on.
His roots are in the energy sector, as Privacy & Security Officer at Liander and co-founder of the European Energy-ISAC. Today he works across critical infrastructure and food production, often as interim CISO. You work with Johan himself, from the first conversation to the last report.
Recent assignments
What colleagues and clients say.
From recommendations on LinkedIn.
“Johan has been one of the most valuable and knowledgeable members of the utility community, being a very active contributor and a leader of the EU movement working for the cyber resilience and privacy-alignment of the sector.”
“I have experienced Johan as a man with drive, focus and a strong capability of initiation and set up of new methods and frameworks in difficult circumstances. … The set up of privacy & security in the area of smart meters within Liander has resulted in the first grid operator in Europe to be 'certified Privacy Proof'.”
“Johan and I worked together on the successful launch of EE-ISAC. … I was impressed by the scope of his network within the European cyber security sector and the way in which he is able to mobilize it in order to reach common goals.”
Where a cyber attack can stop production.
Especially relevant if your organisation falls under NIS2.
Notes from the field.
Recent work and observations from offshore wind, energy and critical infrastructure.
Enhancing cyber resilience in offshore wind
RambiCo is bringing TenneT, wind farm owners and suppliers together to share security information and strengthen cyber resilience in Dutch offshore wind, on behalf of the Field Lab Energy Cyber Security.
Read the articleOne view on IT and OT: building an integrated cyber defence centre
Production systems often stay out of sight of the security team, while attacks rarely respect the line between office and plant. What it takes to monitor IT and OT together.
Read the noteA cyber security roadmap the board can steer on
Many security roadmaps are long lists of technical projects. Lessons from interim CISO roles on building one that starts with the business and fits on a page.
Read the noteNIS2 and ISO 27001 gap assessments: what we find, and what to fix first
Recurring findings from NIS2 and ISO 27001 gap assessments in energy and IT services, and five recommendations to act on before the auditor or the regulator asks.
Read the noteWhat makes an ISAC work: lessons from a decade of information sharing
From the DENSEK project in 2013 to the European Energy-ISAC and new Dutch sector communities: what keeps members sharing, year after year.
Read the noteTrilateral MoU signing at GridSecCon
On 17 October 2018, at GridSecCon in Las Vegas, Johan Rambi signed the trilateral Memorandum of Understanding between the US E-ISAC, Japan's JE-ISAC and EE-ISAC, on behalf of the EE-ISAC chair and…
Read the noteWhere does your organisation stand?
Tell me in a few lines. I'll tell you honestly where I can help, and where I can't. A first conversation is free.
Write to Johan directly
Describe in a few lines what is going on. Johan reads every message himself and replies within two working days.
Write an emailOr call +31 6 11 87 99 45